Tech · Explainer
Google Says Hackers Use AI to Strike Before Users Can Patch
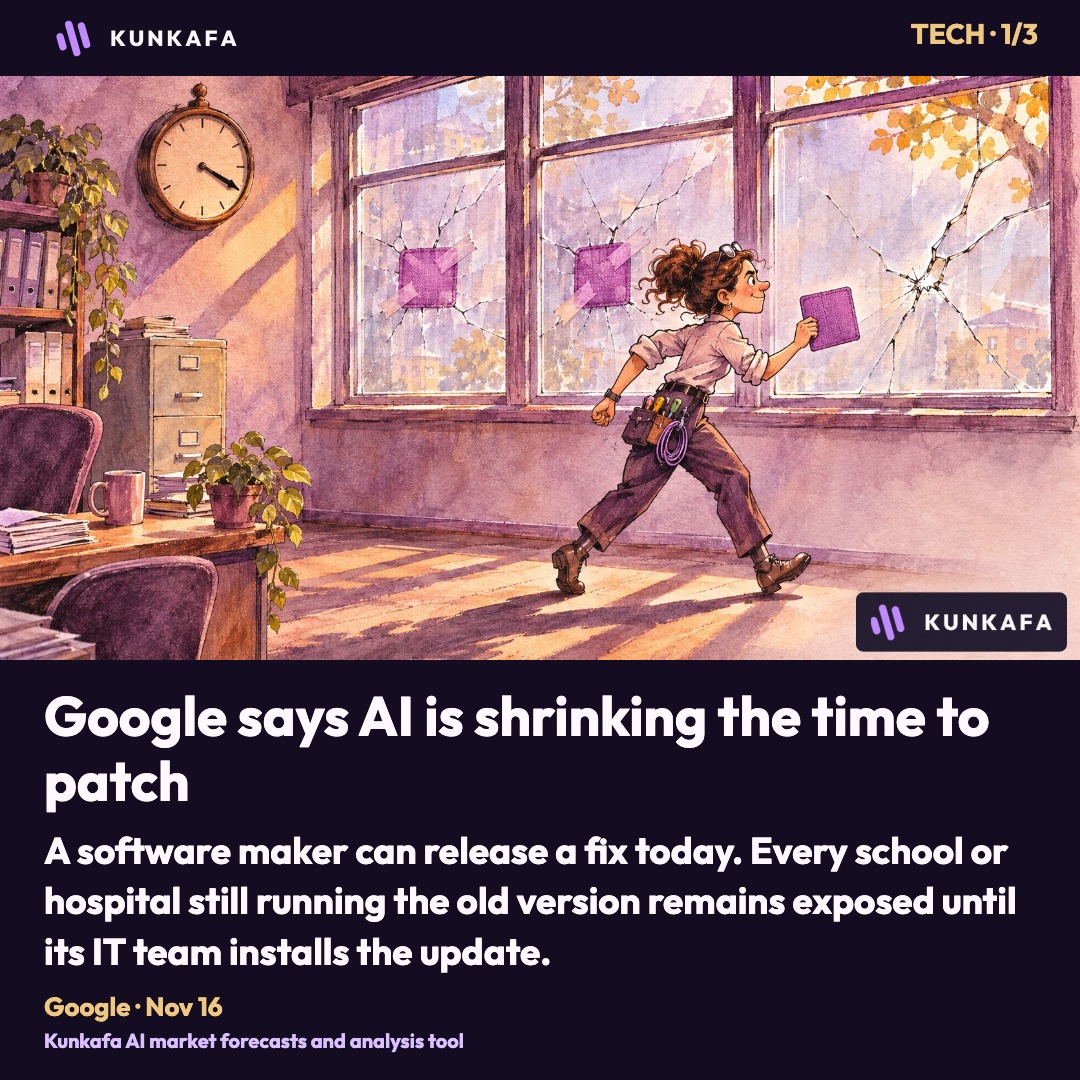
Once a software maker releases a security fix, customers need time to install it. Google’s researchers found attackers using AI to take advantage of that delay.

Kunkafa News · Published · 3 min read
 By Kareem FaridDiscuss with the author on X
Here is a visual story in summary
Key points
- Google found software designed to turn newly disclosed fixes into attacks without a person directing each step.
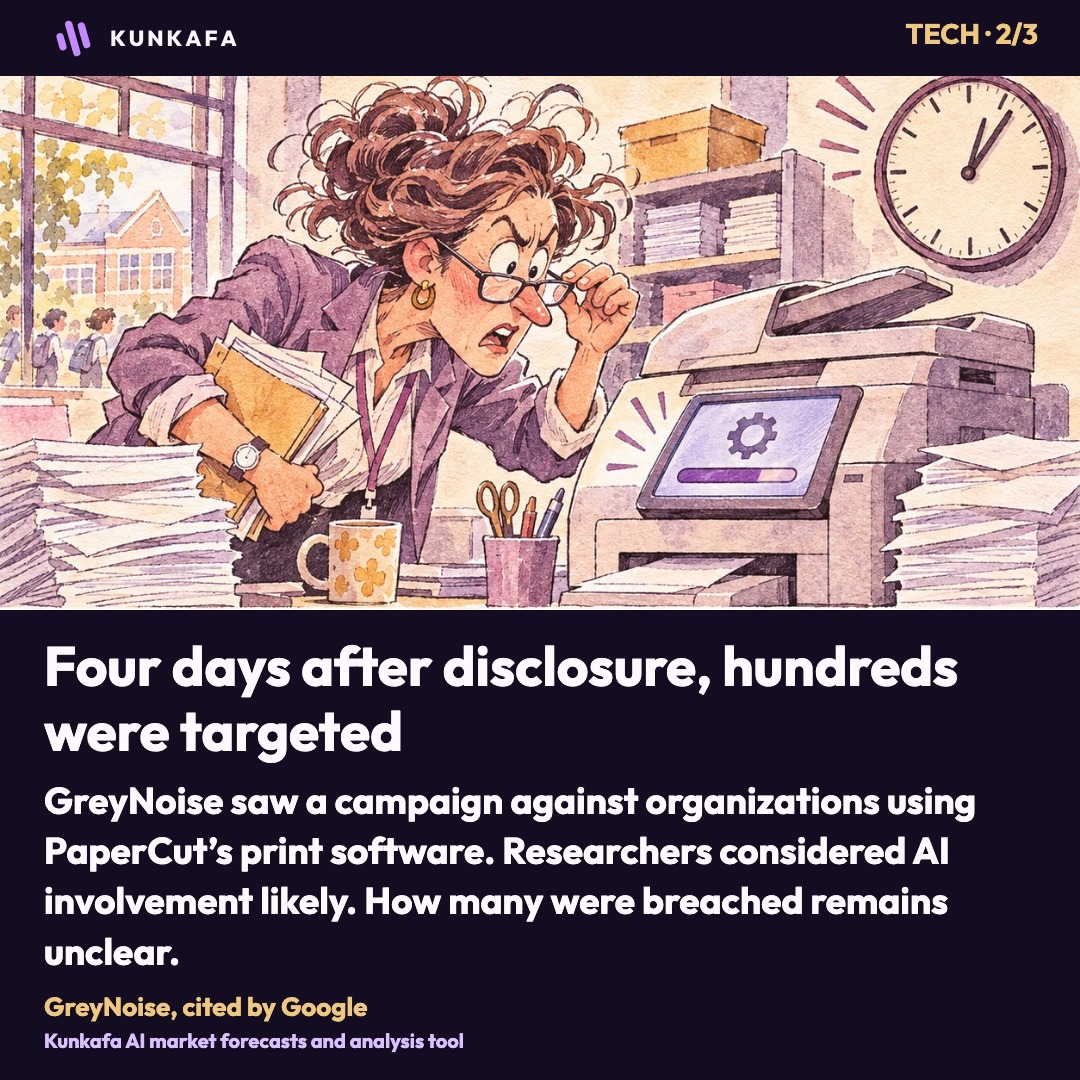
- In one print-software case, a campaign targeted hundreds of organizations four days after disclosure.
Attackers are using AI to strike in the time between a software company releasing a security update and its customers installing it, Google reported on November 16. For a school or hospital, the distinction matters: the vendor may have fixed a flaw while the version running on its computers is still vulnerable. Google’s threat researchers found software designed to exploit that delay without a person directing each step. Google highlighted the finding in a post accompanying the report [1] [2].
Hackers are now using LLMs to continuously scan software updates, spot newly fixed bugs, and build attacks before teams can apply the fix — all without human involvement. That’s according to the latest report from the Google Threat Intelligence Group. We're helping defenders… Show more
What four days meant for PaperCut customers
PaperCut makes software that organizations use to manage printers. Google’s report describes two flaws that attackers had already used in late August, before customers knew about them. Within a day of public disclosure, security researchers showed that AI could help reproduce the attack. Four days after disclosure, the security firm GreyNoise observed a campaign targeting hundreds of organizations. The researchers assessed AI use in that campaign as likely. The number of organizations actually compromised remains unclear [1].
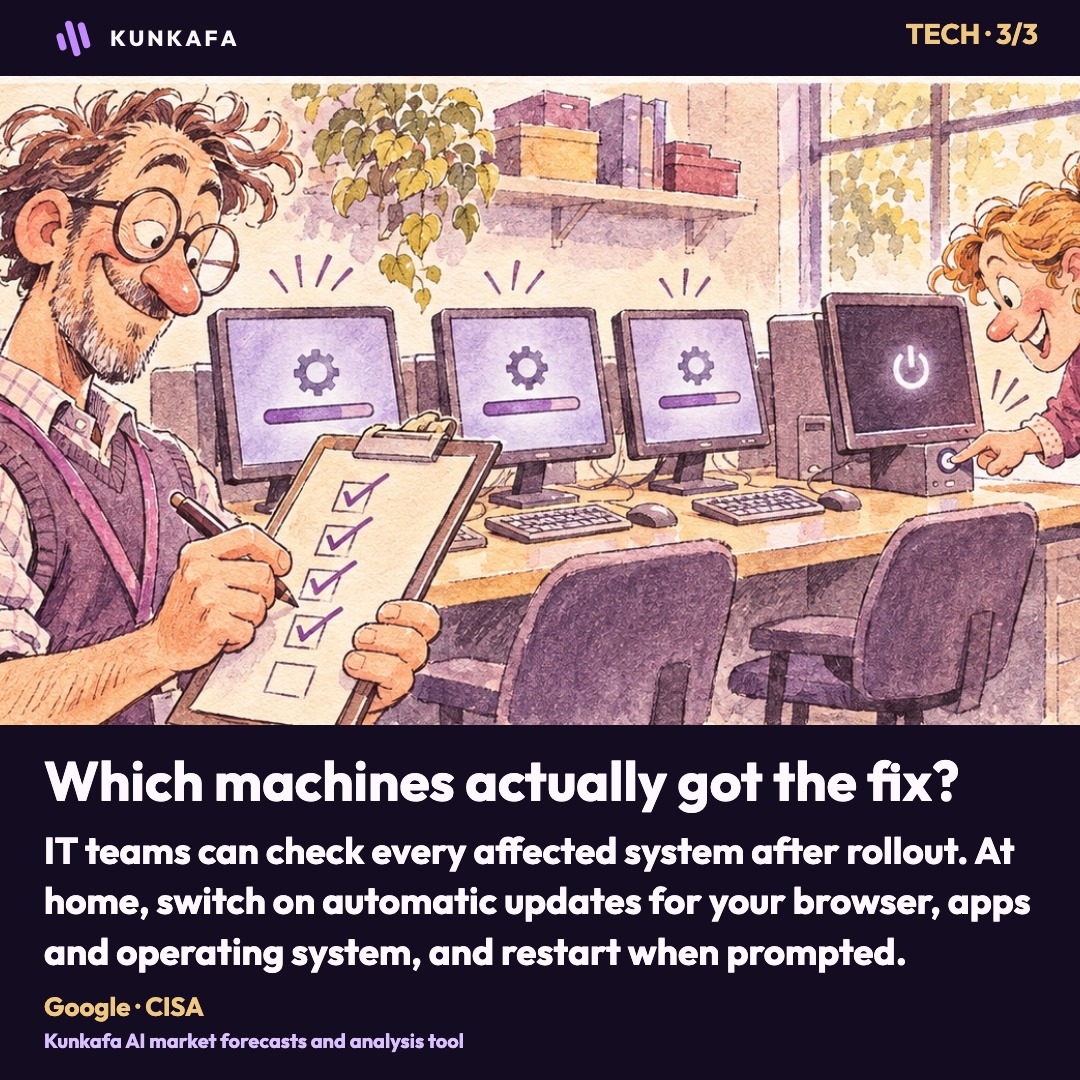
Google is also applying AI on the defensive side. It says its tools can identify vulnerable software, prioritize fixes according to which systems are exposed and help prepare patches. For the organization running that software, the crucial step is checking that the fix actually reached every affected system [3].
Where this fits in recent incidents
In the BBC and Zoom case, visitors could load malicious code on a genuine website because a supplier’s software had been compromised. In the Bitcoin mining incident, Luxor said an attacker diverted mining revenue from customers and that it patched its management software within two hours. The public findings in both cases leave the role of AI unconfirmed. Kunkafa’s developing incident ledger tracks subsequent disclosures, while its five-week review also documents outages that operators attributed to technical failures.
What to update first
On a phone or home computer, turn on automatic updates for the operating system, browser and apps, and complete any restart they request. The US Cybersecurity and Infrastructure Security Agency advises installing critical updates promptly. For an IT team managing many systems, its guidance gives priority to internet-facing services with flaws attackers are already using [4] [5].
Sources: [1] Google Threat Intelligence Group and Mandiant, Nov 16, 2026 · [2] News from Google, Nov 16 · [3] Google, Nov 16 · [4] CISA software update guide · [5] CISA ransomware guide
Kunkafa forecasts
Alphabet
How far it could move, which way, by when, and how confident Kunkafa is.
Check the latest forecastsMore in Tech

Hackers Leak Customer Data Tied to Visa, Mastercard and Chase
Mastercard says emails from a benefits program were exposed. Visa says its systems were unaffected and it has seen no sign that card numbers were compromised.

OrcaRouter’s Shield Fooled an AI Hacker for a Minute in a Test
OrcaRouter says its new Shield tool had already spotted ARTEX by the time the agent recognized the decoy in a test on the company’s own site.

PHP Can’t Catch a Break: Seven New Critical Flaws
Patches are out for four PHP branches, a month after attackers exploited the October flaws. Here’s which version your site needs.